How a playbook is chosen
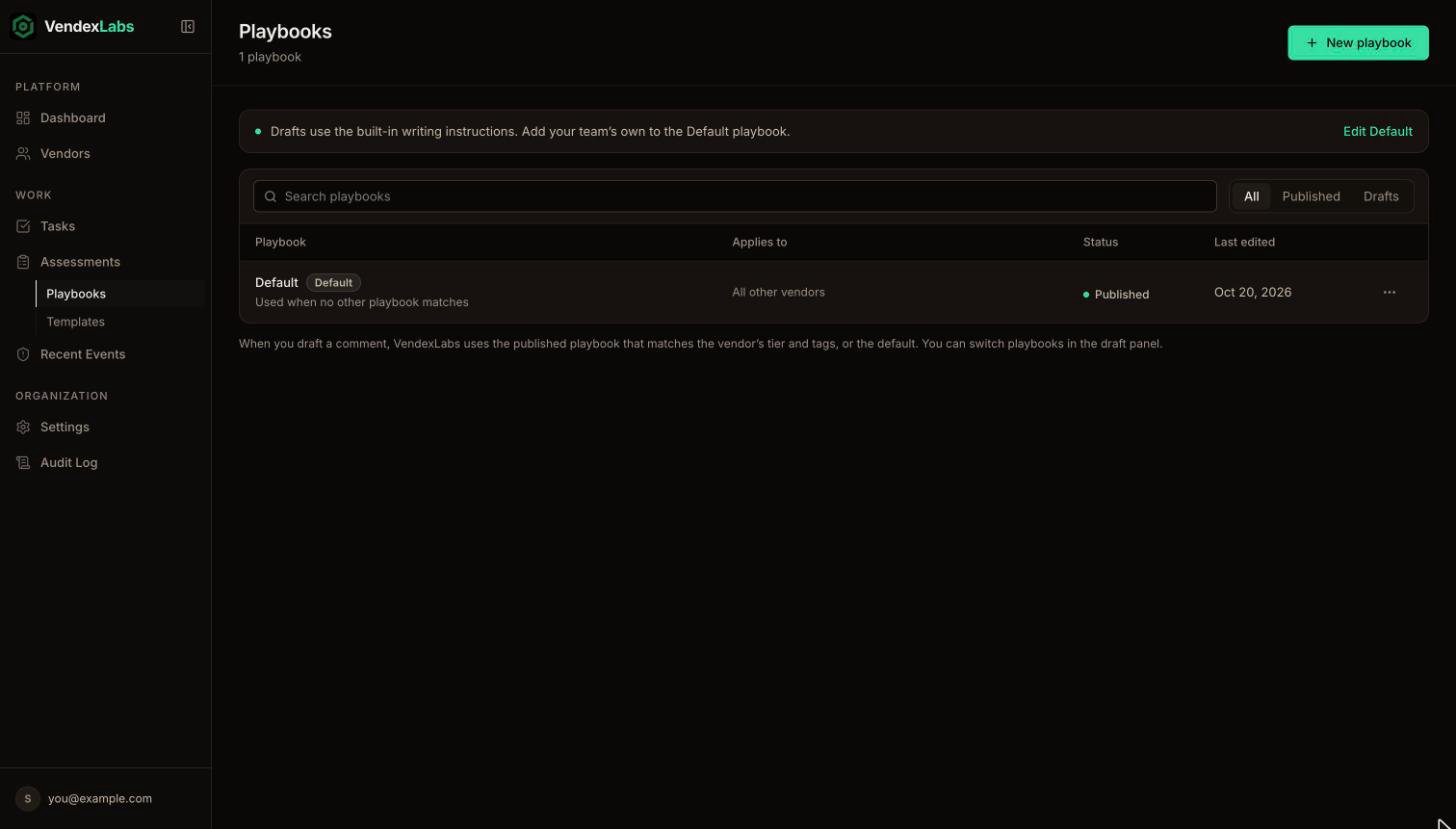
When someone drafts a comment, VendexLabs uses, in order:- The playbook they picked for that draft.
- A published playbook whose dependency tier and tags match the vendor.
- The default playbook, which covers every vendor no other playbook matches.
What’s in a playbook
Applies to
Applies to
The dependency tiers and tags the playbook matches. The editor shows how many of your vendors currently match.
Instructions
Instructions
One set of instructions each for the security risk, compliance, and privacy comments. Write them the way you’d brief a colleague. Built-in rules always apply on top: every fact is cited, nothing is invented, and only the compliance comment suggests an outcome.
Reference document
Reference document
Optionally attach a text PDF (up to 5 MB), such as your vendor risk policy, for drafts to follow.
Sources
Sources
What drafts may draw on besides the assessment’s own evidence review: business context, enrichment research, and past comments to write like.
Freshness
Freshness
Search the web for recent findings adds cited breach, certification, and enforcement news. Drafts are slightly slower with it on.
Structure
Structure
The length and shape of every comment drafted with this playbook.
Template
Template
Optionally, the template that usually goes with this playbook.
Drafts and publishing
Drafts aren’t used automatically until an admin publishes them. Only admins can change a published playbook, so to propose a change, create a new playbook as a draft. Archiving a playbook stops drafts from using it.